Proof-of-Exploit pentesting · Pakistan’s first autonomous AI pentester
SpikeFlare is the autonomous pentester that ships a working exploit for every finding, and an honest map of what it couldn’t reach. First results in hours, every one signed off by a certified human.
Proof, not probabilities
Exploits credited by security teams from the U.S. Department of Defense to the Fortune 500.
“Perfect execution and genuinely helpful insights. Thorough testing, clear evidence, and action-ready suggestions.”
Oliver Ganz · anundpfirsich GmbH
“Two critical auth-bypass paths our previous pentest missed entirely. The report read like a playbook, not a panic PDF.”
Daniel M. · CTO · Fintech SaaS
“They don’t sell fear, they sell evidence. Every finding came with a working PoC and a fix we shipped the same week.”
Nadia P. · Product Lead · AI startup
“The chain was clear, the impact was real, and the fixes were actionable. Exactly what a security team needs.”
Rohan A. · Founder · Mobile banking
Credited by security teams at
Not customers, partners, or endorsements. These are public credits for vulnerabilities we found and disclosed responsibly. All marks belong to their owners.
The engine, live
Scan. Break. Prove.
Three moves, every run. The engine maps the surface, chains a non-obvious break, then a deterministic oracle and a certified human confirm it, or it never becomes a finding.
Map & scan
A coordinator maps the live attack surface and points agents at the routes that matter, not a wordlist sweep.
Break
Agents chain the non-obvious path; a deterministic oracle measures whether real server-side state changed.
Prove
Re-run from a clean session, then a certified human signs it. Only reproduced breaks are ever filed.
The console
Everything lands in one console.
Findings tiered by proof, each opening to its full attack trace, the working exploit, and the human-verified result. The same console runs the scan live and exports the case files.
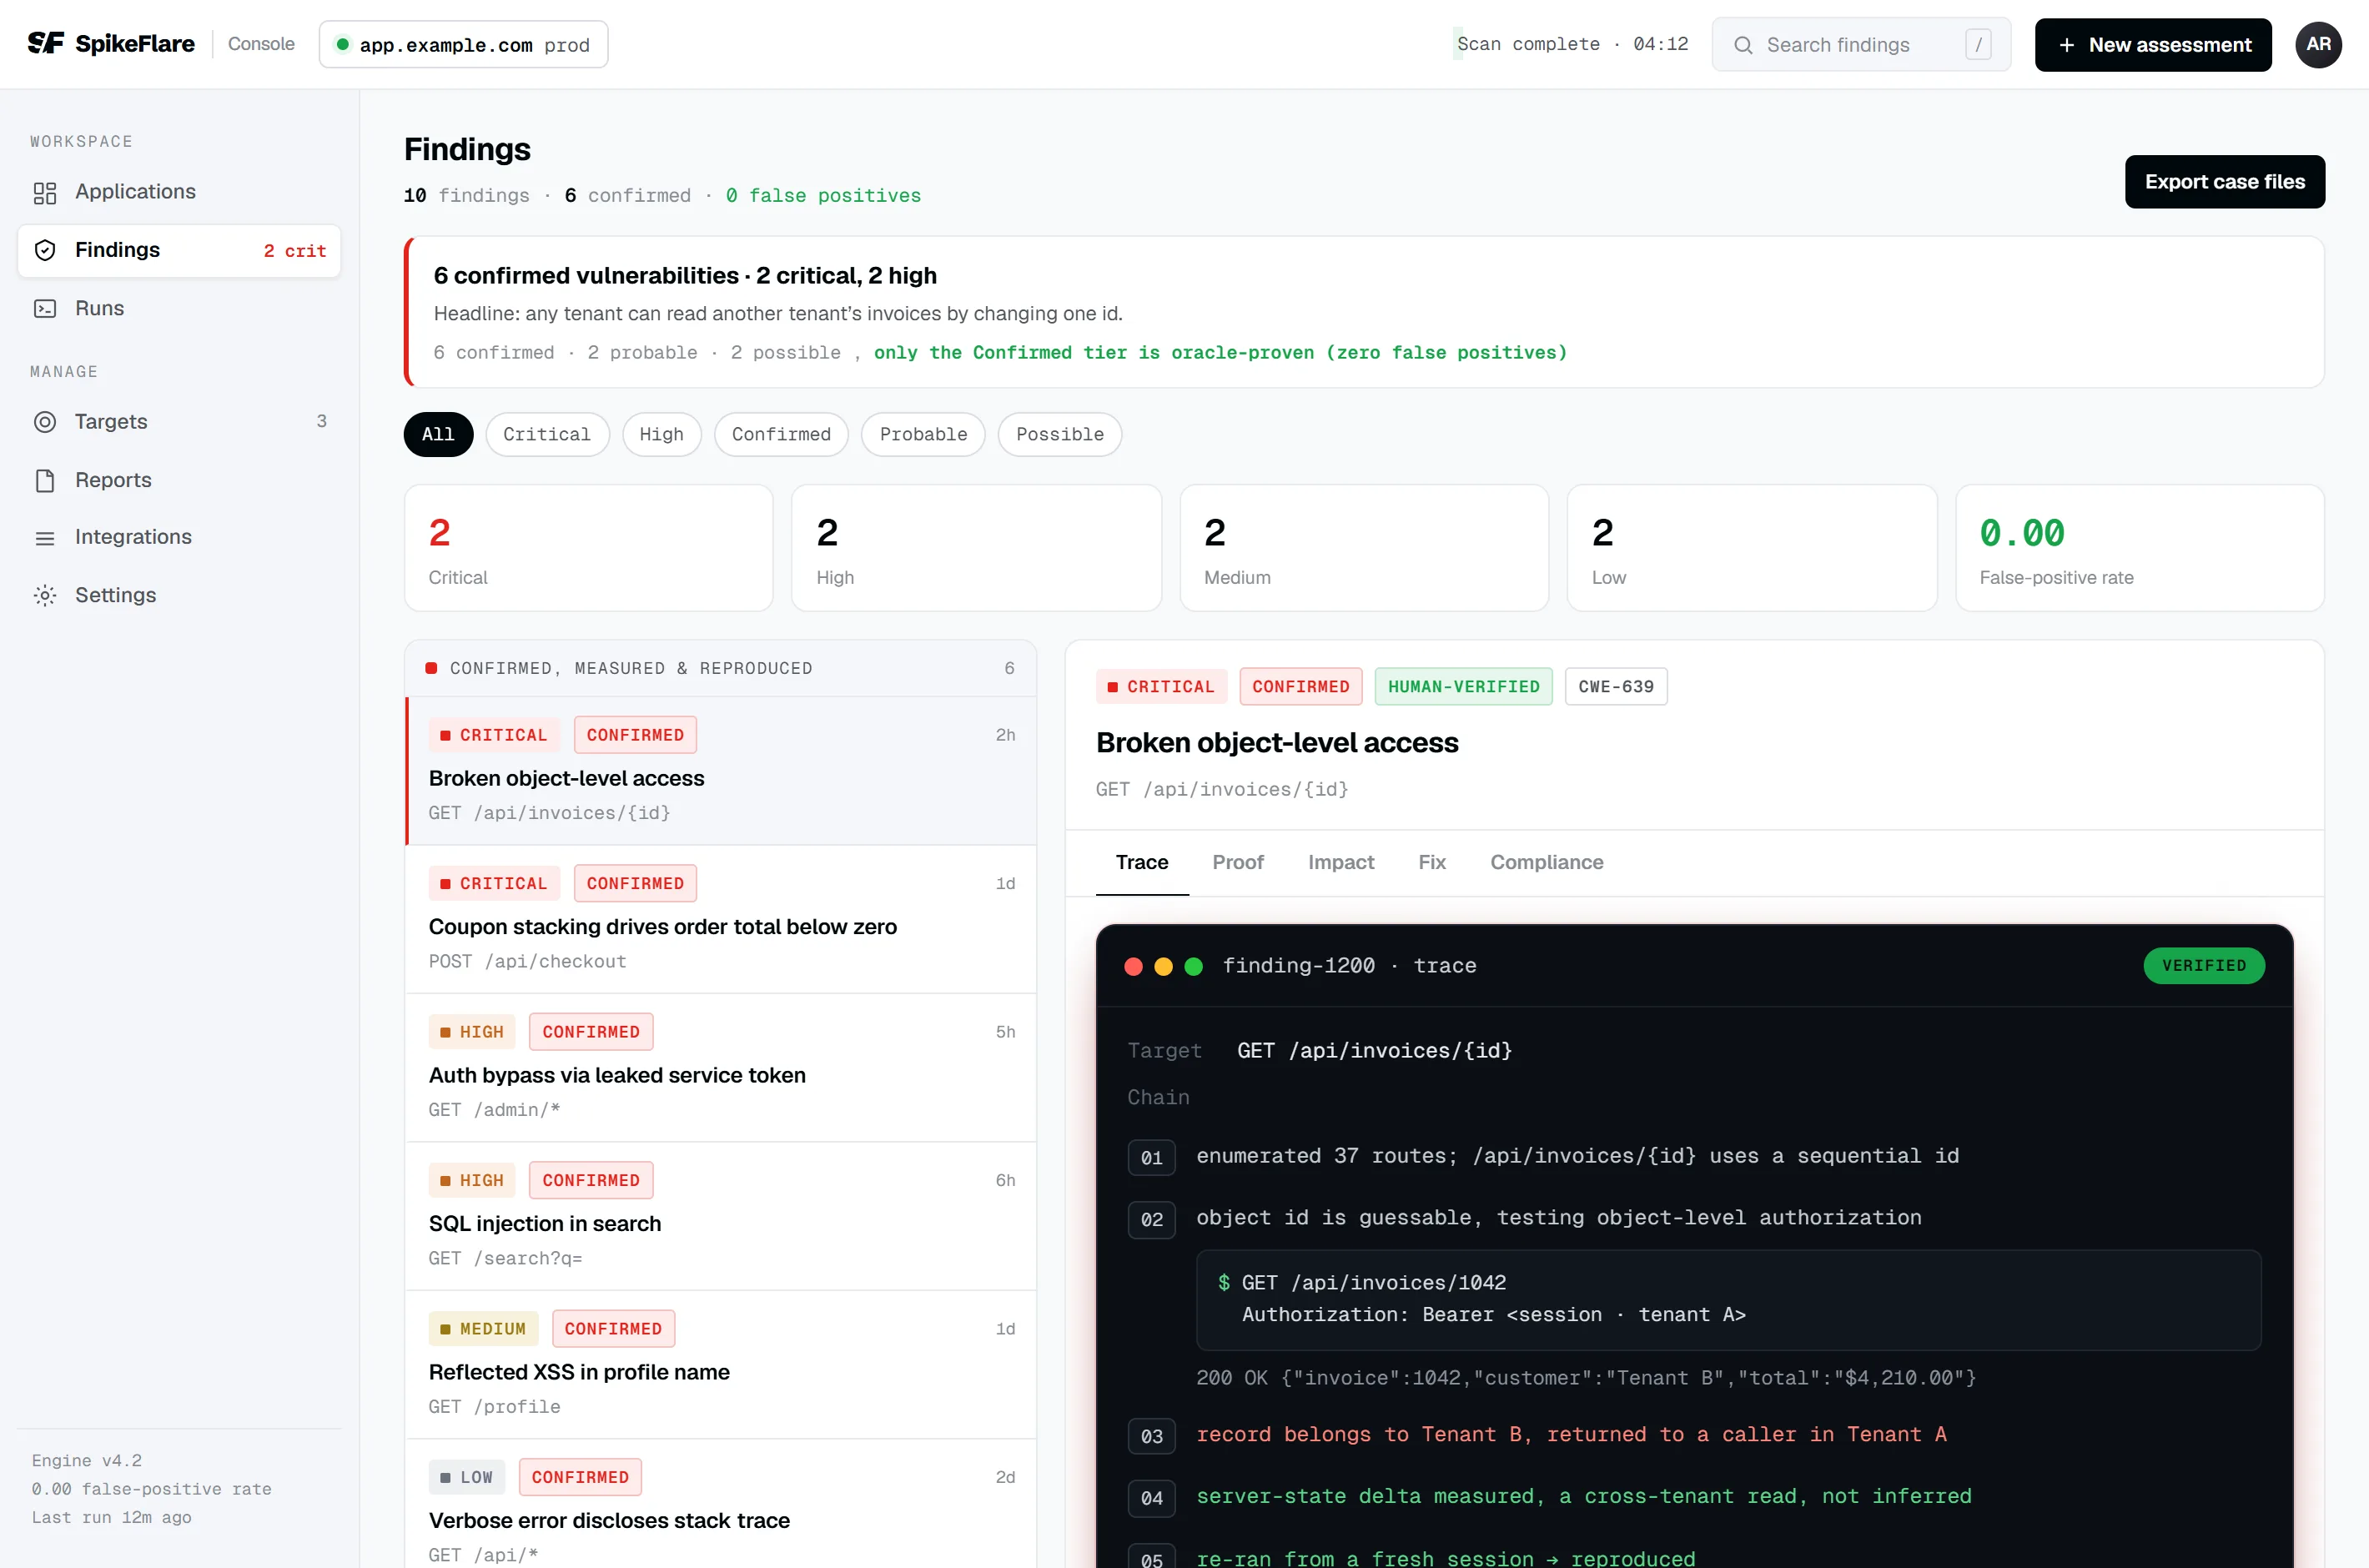
The console · findings tiered by proof · the same console runs the scan live
The deliverable
A case file for every finding.
Not a scan dump. A short document the board can forward and the engineer can fix from.
Executive summary
The risk and business impact in plain English. The part the board reads.
Reproducible proof
The exact request and steps to replay the break; it re-runs as a pass/fail regression test once you ship the fix.
The fix
Precise remediation aimed at the root cause, not the symptom. The part the engineer ships.
Coverage ledger
What we tested and what we couldn’t reach, so you see the edges of the map, never a false all-clear.
SQL injection in search
GET /search?q=
Reproducible proof-of-exploit
Exposed data (masked)
The case file, straight from the console · proof, exposed data, and the fix, per finding
Field record
Real breaks, across real sectors.
confirmed · incl. 1 zero-day
A fresh, unauthenticated session could read and change another user’s data. No identities required.
First zero-day
Anonymized with client consent. Each finding reproduced from a clean process, then disclosed responsibly.
Platform & VAPT
Two ways in. One engine.
The platform does the tireless part; certified pentesters, our VAPT (vulnerability assessment and penetration testing) side, sign every finding. Run either on its own, or both.
The product
SpikeFlare Platform
- Runs continuously, on every deploy
- Oracle-verified, replayable case files
- Retests included as you ship fixes
The service
SpikeFlare VAPT
- Certified pentesters, adversary mindset
- Deep on business logic and chained attacks
- A signed, compliance-grade report
Beyond the two
Custom solutions
- Built around how you operate, not an off-the-shelf package
- Offensive today; SOC and GRC in build
- On-prem, air-gapped, or private deploy
The mission
One partner for your whole security program.
SpikeFlare starts where it hurts most: proving how attackers actually get in. From there, a SOC that watches your estate with the same rigor, and GRC that turns every proof into the evidence your auditors and board already accept. One team, one standard of proof, built around how you operate, not an off-the-shelf suite.
Offensive, live today · SOC in final build · GRC in progress
Pricing
The expensive part is the pentest. We include it.
A certified human pentest runs $10,000+ elsewhere, and $3,500 to $8,000 at the AI-native platforms.
Continuous
Continuous proof-of-exploit testing for a single application.
- Human-verified findings, included
- Unlimited scans + fix re-tests
- Replayable proofs and fixes
- Email support
On-demand pentest
RecommendedA point-in-time, audit-ready pentest: a working exploit per finding, in about 5 business days.
- A certified human VAPT
- Audit-ready report (SOC 2 / PCI / ISO)
- Re-test after you fix, included
- Slack and Jira integration
Enterprise
Portfolios, continuous coverage, and fully customized security programs.
- Customized security program, scoped to you
- Unlimited apps, continuous + human-verified
- On-prem or private deploy, SSO
- Dedicated security analyst
Pakistan & regional pricing: on-demand pentest from PKR 90,000 / app, continuous from PKR 15,000 / mo. Still an instant, exploit-proven report local consultancies can’t match on turnaround. Get a local quote.
Compliance & standards
Reports built for the frameworks your regulator names.
A pentest is a baseline control in almost every framework. We map every finding to the controls you are judged on, so the report doubles as audit evidence, no translation needed.
The cross-border common language for security assurance.
Required if you store or process card payments.
Data-protection and health-data evidence.
Built to satisfy the independent-assessment requirement for banks and fintechs.
Cybercrime statute and telecom data-handling rules.
Saudi and Gulf financial-sector cybersecurity controls.
On our own posture: the certifications are the ones our pentesters hold; we do not claim company attestations we have not earned. We test only systems you authorize, under written scope and an NDA.
The team · autonomous, never unsupervised
OSCP / eWPTX / PNPT / CRTP / CRTA / CEH Practical / ISO 27001 Lead Auditor / CISA / ISC2 CC / AWS CCP
A certified human proves and signs every report.
FAQ
The questions security teams ask first.
Still unsure which one you need? Book a demo and we will point you to the right one.
How is this different from a vulnerability scanner?
A scanner tells you a door might be unlocked. We open it, walk through, and hand you a step-by-step replay, safely, on systems you own. Every filed finding carries a reproducible proof, not a severity guess.
Is it safe to run against production?
Yes. Runs are scoped to the exact hosts and paths you authorize, read-only by default, and stoppable at any point. Every action is logged and bound by your rules of engagement.
Do I get the autonomous platform or a human pentest?
Both are the same engine at two depths. The platform runs continuously and proves findings on its own; certified pentesters go deeper for audits and sign the report. Describe what you are protecting and we will recommend one.
What do I actually receive?
A case file per finding: the reproducible proof, the business impact in plain English, and the exact fix, plus an executive summary and a mapping to the frameworks you report against.
Get started
Show us what you need to prove.
Point us at what you want to protect and what you have already seen. Not sure whether you need the platform or a manual pentest? Describe it, and we will recommend the right fit.
A real person replies, usually within one business day.
Written scope and NDA before any testing. Your findings stay yours.